How to Know If Your Business Needs a Cybersecurity Risk Assessment
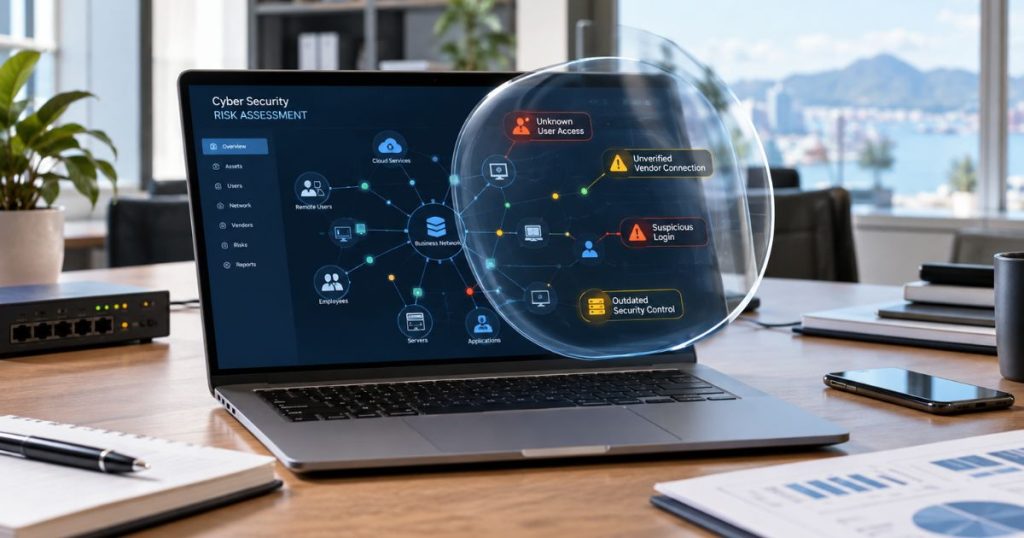
Your business needs a cybersecurity risk assessment when your insurance or compliance requirements are changing, customers start sending detailed security questionnaires, you can’t clearly say who has access to your systems, or you’ve had a close call that made everyone nervous. None of these signs are dramatic on their own. That’s exactly why people miss them.
Most businesses don’t schedule a cybersecurity risk assessment because they woke up thinking about security. Something external usually forces the question, a renewal form, a procurement team, a strange login at 2 am. By then, you’re reacting under a deadline instead of choosing to look closer on your own terms. This guide walks through the seven signs that tend to show up first, what a risk assessment actually involves, what it costs, and how to decide whether to run one internally or bring in a third party.
What Is a Cybersecurity Risk Assessment?
A cybersecurity risk assessment is a structured review of your systems, data, access controls, and processes that identifies where your business is exposed to cyber threats and ranks those exposures by likelihood and potential impact. It’s the process businesses use to turn a vague sense of “we should probably do something about security” into a specific, prioritised list of what to fix first.
It’s worth distinguishing this from an early security audit, because the two get used interchangeably and shouldn’t be. A risk assessment asks what could go wrong and how bad it would be. An audit asks whether the controls you already claim to have are actually working and compliant. Most businesses need both eventually, but they answer different questions, and an information security risk assessment is usually the right place to start because it tells you where to point everything else.
Why Cybersecurity Risk Assessments Matter for Small and Medium Businesses
Small and medium businesses in New Zealand and Australia are past the point of assuming they’re too small to be worth attacking. New Zealand’s National Cyber Security Centre found that 53% of NZ small and medium businesses experienced a cyber threat in the first half of 2025 alone, up from 36% the year before, with direct financial losses across all reported cybercrime reaching NZ$26.9 million for 2024/25. In Australia, the ASD’s 2024–25 Annual Cyber Threat Report recorded an 11% rise in serious incidents and put the average self-reported cost of cybercrime to a small business at A$56,600, up 14% on the year before.
Regulators are watching the same trend. The OAIC logged 1,205 data breach notifications in 2025, the highest since Australia’s Notifiable Data Breaches scheme began in 2018. Under New Zealand’s Privacy Act 2020, any business holding personal information must notify the Privacy Commissioner and affected individuals when a breach is likely to cause serious harm. Cybersecurity risk management isn’t a technical nicety anymore. It’s what lets you show, in writing, that you understood your exposure before something happened, not after.
7 Signs Your Business Needs a Cybersecurity Risk Assessment

These seven signals show up across NZ and AU businesses well before a breach forces the conversation. Spotting even one of them is usually reason enough to act.
1. Your Cyber Insurance or Compliance Requirements Are Changing
Cyber insurance renewals used to be a formality. Now insurers routinely ask for specifics on multi-factor authentication, backup testing, endpoint protection, and how you’d respond to an incident, and they want evidence, not a checkbox. If you’re also working toward a framework like ISO 27001, SOC 2, or the NZ Privacy Act’s 13 Information Privacy Principles, the honest answer to “can you prove that control exists” is often “we think so.” A compliance reporting service built around your specific framework closes that gap before a renewal or audit forces the question.
2. Customers or Vendors Are Sending Detailed Security Questionnaires
The bigger the deal, the more likely a prospective customer is to send a security questionnaire before signing anything. These ask whether you use MFA, how you handle their data, whether you’ve had incidents, and whether you can produce documentation on demand. If answering means pulling three people into a call to reconstruct what you actually do, that uncertainty is already costing you deals. A documented third-party risk management approach, the same likelihood-and-impact logic you’d use to assess a vendor, applies just as well to preparing answers for when you’re the one being assessed.
3. You Can’t Clearly Say Who Has Access to Your Systems
Access sprawl happens quietly. A contractor gets temporary access that’s never revoked. Someone changes roles but keeps their old permissions. A shared login becomes normal because rotating it is inconvenient. None of this looks like a crisis day-to-day, which is exactly why it survives so long. If you can’t produce a current, accurate list of who can access your customer records, financial systems, and core business applications, a network security risk assessment is the fastest way to see how far that gap has spread.
4. Your Business Has Grown, Added New Tools, or Changed Vendors
New hires, a cloud migration, a new CRM, a merger, remote work: each of these expands what needs protecting, and the controls that made sense two years ago rarely scale cleanly with the business. Post-acquisition IT integration is a particularly sharp version of this, since you inherit whatever vulnerabilities the other party had the moment your systems connect. Verizon’s 2025 Data Breach Investigations Report found third-party involvement in confirmed breaches doubled year over year, from 15% to 30%, directly reflecting how much risk businesses absorb every time they add a vendor or partner without checking first.
5. You’ve Had a Near-Miss Incident or Suspicious Activity
A phishing email that almost got a click. A login from a country nobody recognises. A data export nobody remembers authorising. Near-misses are the most useful signal you’ll get, because they confirm a gap exists while the details are still fresh enough to trace. Acting on one immediately, while logs are intact and people remember what happened, is far more effective than revisiting it in six months once the trail has gone cold. If you don’t already have a documented cyber security incident response plan, a near-miss is the moment to build one, not the moment after the next one succeeds.
6. Your Security Documentation Is Outdated, Missing, or Scattered
Most businesses have some security documentation. It’s just spread across a shared drive, a vendor’s admin portal, and someone’s memory. Having a control and being able to produce evidence of it are different problems, and the gap between them is usually bigger than people expect until an auditor, insurer, or customer asks for the paperwork directly. A cyber security risk assessment checklist forces that separation early, sorting what’s actually documented from what everyone just assumes is true.
7. Leadership Can’t Confidently Answer Basic Security Questions
This is often the clearest sign because it shows up in a boardroom rather than a server log. Leadership doesn’t need to understand every technical control, but should be able to answer a handful of plain questions: what’s protecting the business right now, what evidence backs that up, where are the biggest gaps, and who owns fixing them. If those answers come back vague, that’s not a failure. It’s a common cybersecurity risk profile for a growing business, and a structured review is designed to replace it with specifics.
How to Identify Cybersecurity Risks in Your Business
Identifying cybersecurity risk starts with an honest inventory: what systems, data, and vendors you actually have, not what you assume you have. From there, assess three things for each asset: the realistic cybersecurity challenges it faces (ransomware, phishing, insider misuse, or vendor compromise); how likely each is given your current controls; and what it would cost if it happened. Ranking risks by likelihood and impact, rather than chasing whatever feels most urgent that week, is what turns a vague worry into a prioritised action list.
What a Cybersecurity Risk Assessment Actually Involves
A properly run assessment follows a consistent sequence: mapping the assets that need protecting, analysing the threats most relevant to your business, scanning for technical and process vulnerabilities, scoring each finding by likelihood and impact, and producing a prioritised remediation roadmap rather than a 50-page list with no clear starting point. The output should translate technical findings into language a business owner or board can act on. CyberMark’s own structured cybersecurity risk assessment and audit process follows this sequence and maps findings against the frameworks that matter for NZ and AU businesses, including ISO 27001, SOC 2, the NZ Privacy Act 2020, and Australia’s Privacy Act 1988.
How Much Does a Cybersecurity Risk Assessment Cost?
Globally, pricing varies widely because assessments aren’t standardised. Industry benchmarks put a limited, narrow-scope small-business assessment at roughly US$1,000 to US$5,000, a fuller consultant-led review with interviews, evidence checks, and a written report at US$5,000 to US$15,000, and larger compliance-driven, multi-site engagements above that. These are planning ranges, not a fixed price list, and they shift with scope, industry, and how many frameworks need mapping.
For a concrete NZ reference point, CyberMark’s baseline cybersecurity risk assessment starts at around $2,000 NZD, with individual compliance framework assessments (NZ Privacy Act 2020, HIPAA, GDPR, AU Privacy Act) priced from $500 NZD each. Businesses juggling more than one framework are often better off assessing them together, since overlapping controls reduce the total cost rather than paying twice for the same evidence.
Internal Team vs Third-Party Cybersecurity Risk Assessment: Which Is Right for Your Business?
Internal assessments are faster and cheaper, and your team already knows the environment. The limit is what your team doesn’t know it doesn’t know. Even a technically strong internal IT person may not be tracking the newest attack patterns targeting your industry, and self-assessment naturally struggles with objectivity: it’s hard to flag your own blind spots when you built the system.
A third-party assessment trades some of that speed for an independent, credentialed view. An outside provider isn’t invested in defending decisions your team already made, which tends to surface issues an internal review normalises or simply doesn’t see; third-party findings also carry more weight with insurers, regulators, and boards. Many businesses land on a hybrid: an internal team handles day-to-day monitoring, while an independent review runs annually or after any significant change. When the assessment surfaces gaps in ongoing monitoring rather than one-off findings, managed detection and response services are usually the logical next step, since continuous coverage keeps a point-in-time assessment from going stale.
Frequently Asked Questions
What are the 5 steps of a cybersecurity risk assessment?
Define the scope and assets in play, identify relevant threats and vulnerabilities, assess likelihood and impact, prioritise findings against controls, and build a remediation plan with owners and timelines. This shape holds across NIST, ISO 27005, and most vendor methodologies.
What are the 5 pillars of risk assessment?
Under the NIST Cybersecurity Framework, the five core functions are Identify, Protect, Detect, Respond, and Recover. These are categories of control, not a sequence of steps, so they sit alongside rather than replace the 5-step process above.
What tools are used for a cybersecurity risk assessment?
A typical assessment combines vulnerability scanners, configuration review tools, access management reviews, and manual interviews to catch policy gaps scanners can’t see. Human analysis on top of the scan results matters as much as the scan itself.
What are the top cybersecurity risks small businesses face today?
Phishing and business email compromise are the most common entry points, followed by ransomware, credential theft, insider risk, and third-party or vendor compromise.
What are the 5 C’s of cybersecurity?
The 5 C’s are Change, Compliance, Cost, Continuity, and Coverage, a commonly used industry framework rather than a government or standards-body one. It covers staying current, meeting regulations, weighing spend against risk, staying operational, and covering the full environment.
What is the role of risk assessment in cybersecurity?
A risk assessment turns cybersecurity from a general worry into a specific, defensible plan. It tells you which threats matter most to your business, what they’d cost, and what to fix first within your budget.
How do I do a risk assessment for my business?
List every system, application, and data store you rely on, along with who has access to each. Score each threat by likelihood and impact, then rank the results. Most smaller businesses start this internally before bringing in a third party to validate findings.
How often should a business get a cybersecurity risk assessment?
An annual assessment is a reasonable baseline for most small and medium businesses. Higher-risk or regulated businesses should add a lighter quarterly review, and any major incident or change should trigger a fresh look regardless of timing.
Is It Time for a Cybersecurity Risk Assessment for Your Business?
If any of the seven signs above sound familiar, one of them alone is usually enough reason to act. The pattern across all of them is the same: uncertainty that’s currently invisible because nothing has gone wrong yet. A cybersecurity risk assessment doesn’t mean your current security has failed or that your IT provider dropped the ball. For most NZ and AU small and medium businesses, needing one is simply a sign of growth, an insurer asking sharper questions, or a customer base that’s grown large enough to expect proof rather than reassurance.
The businesses that get caught out are almost always the ones that waited for an incident before asking the question. If you’d rather ask it on your own terms, book a free security assessment consultation and get a clear, independent picture of where your business actually stands before anyone else asks you to prove it.
Need help reducing your business security risk?
Contact us

